
AI is changing how software gets built. Code is generated, changed, and shipped faster than ever, but penetration testing often remains a periodic exercise.
Security teams need security practices that keep pace with development and help them focus on the risks that matter most.
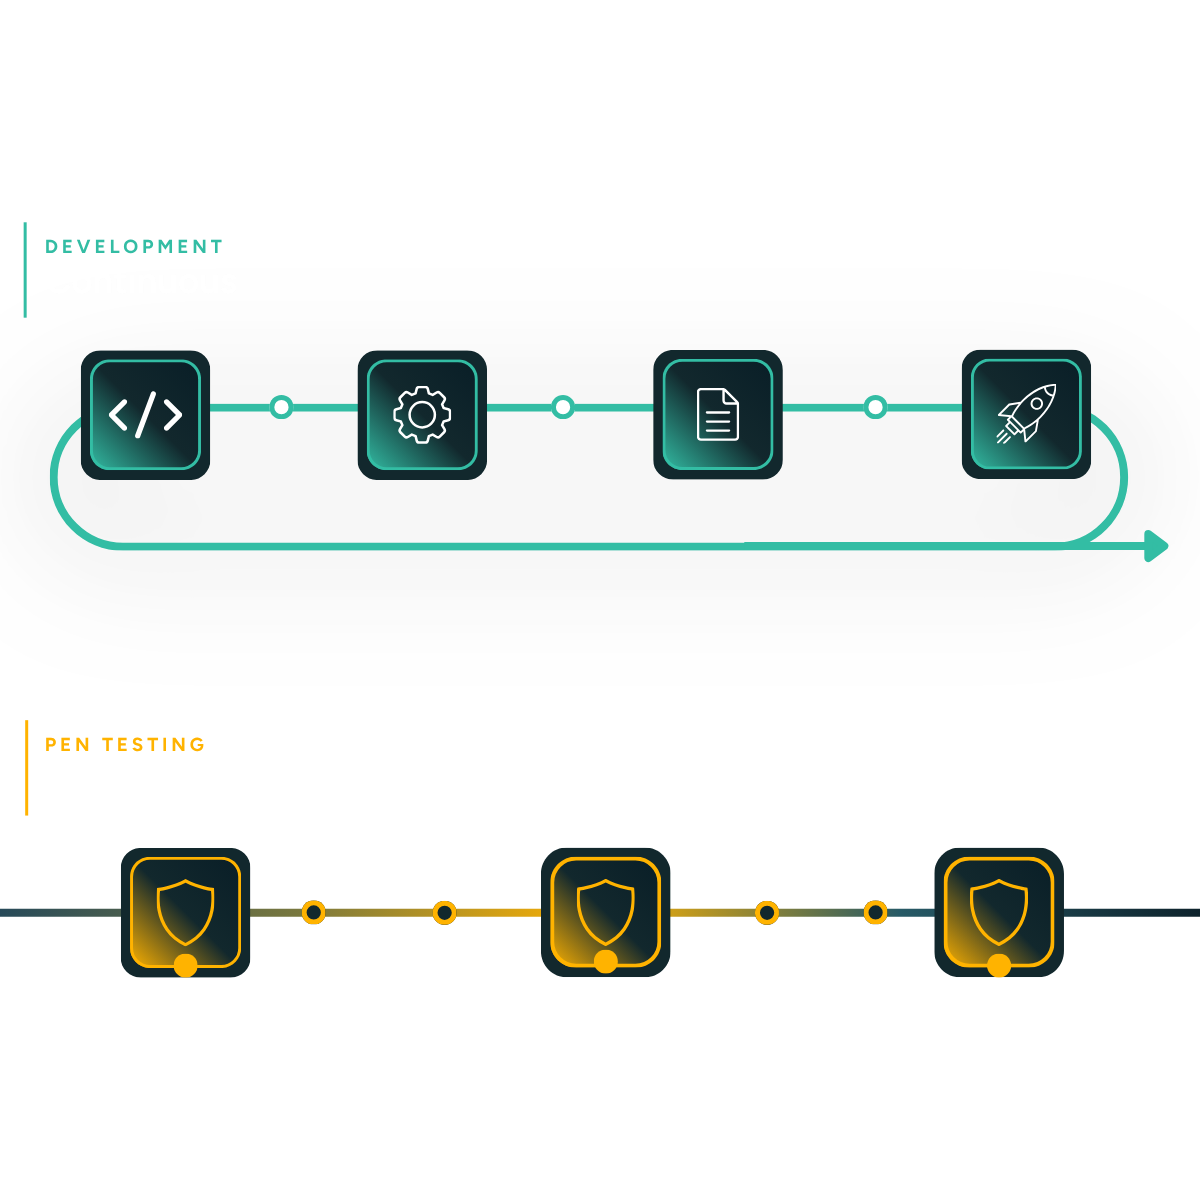
AI coding tools are changing how quickly teams generate, modify, and ship software.
Traditional penetration tests often assess an application at a point in time, while the code and attack surface continue to change.
Identifying a vulnerability is important. Understanding its potential impact and exploitability helps teams make better security decisions.
More code and more findings don't automatically mean better security. Teams need context to distinguish exploitable, high-impact risks from issues that can wait.
Bring security into the entire development lifecycle—from the AI agent generating code to the developer responsible for fixing it.
SEE ARNICA IN ACTION